Headless browser vs real browser for AI agents

Choose browser visibility, authorized account state and execution location separately. A headless browser can reuse approved saved state, while a visible browser can start empty. Use a visible session when the task needs inspection or takeover, and an unattended runner when its result can be checked without a window. Neither mode grants access or defeats site controls.
For permitted batch work, measure the cost of the actual browser and workload. For account work, identify who owns the state and where it lives. ego(lite) offers a visible local task Space and takeover; this does not constrain every tool the host Agent can call or keep every observation on the device.
Headless means no visible browser window. Headed means a window is displayed. A persistent profile and an approved storage-state file are separate ways to retain account data. This article uses real browser for an interactive browser environment, not as a promise of an existing login, isolation or permission.
Everything below is the evidence: the concrete tools on each side by name starting with the real-browser side, then the three deciding dimensions in depth (logins, detection, cost), and a task table you can pick from directly.
Match the browser to the task, not to a preference.
How do you decide: real browser or headless?
Choose display mode, account state and execution location separately. Modern Chrome shares its browser implementation between headless and headed modes. A visible window does not import a login; a headless context can use authorized saved state. Use a visible local browser when the task requires human inspection or takeover, and headless execution when an unattended job can verify its result without a window.
The official Chrome guide dates unified headless to Chrome 112. Since Chrome 132.0.6793.0, the old implementation is available only as the separate chrome-headless-shell binary. Comparing an old shell with a current desktop browser changes more than visibility. Record the browser build, controller and profile before attributing an outcome to headless mode.
This November 11, 2026 maintenance review checked the vendor documentation, not a new detection or login experiment. The August login runs and the three-mode detector case below remain historical observations on their recorded versions. They cannot establish a current success rate or isolate visibility as the cause of a difference.
| Decision | Available choices | What to verify |
|---|---|---|
| Display | Headless or visible window | Does the task need visual inspection or human takeover? |
| Account state | Fresh context, authorized saved state or deliberate profile connection | Which account is active, and has its state expired? |
| Execution location | Local machine or hosted runtime | Where do cookies, downloads and observations travel? |
| Controller | Library, MCP server or browser skill | Which runtime instructions and permissions apply? |
- Chrome headless implementation and old-shell boundary
- Playwright saved authentication state
- Puppeteer Chrome and Firefox protocol support
Do agents need a persistent computer, not a sandbox?
For a one-shot script, an ephemeral sandbox is usually the right boundary. For an agent that returns tomorrow, a persistent computer is the more useful mental model: it keeps a filesystem, installed packages, browser profile, and task state between runs. Cloudflare describes this distinction as giving each agent a computer rather than only a container, while LangChain makes the same case for a filesystem, shell, package manager, and persistent state. Cloudflare's explanation and LangChain's runtime perspective spell out the infrastructure trade-off.
Persistence is not a reason to remove isolation. The useful design is an isolated, user-authorized workspace whose state survives the task, with explicit reset and handoff controls. A sandbox protects the host from untrusted code; a persistent computer protects the agent's continuity. They solve different problems and can be layered together. CNCF's analysis of agent sandboxing makes the same point: execution isolation alone does not provide the durable environment an agent needs for multi-step work. Read the CNCF analysis for the isolation context.
| Environment | What survives | Best fit | Main question to ask |
|---|---|---|---|
| Ephemeral sandbox | Only the outputs you explicitly export | Untrusted code, CI, one-off jobs | What must be saved before teardown? |
| Persistent computer | Files, packages, memory, and browser state | Long-running, resumable agent workflows | Who can inspect, reset, or revoke it? |
| Isolated real-browser Space | An authorized profile and its live sessions | Account work that needs continuity and oversight | Is the action still user-approved? |
An interactive local browser is useful when the task deliberately reuses an authorized account and needs inspection or takeover. ego(lite) can keep that browser state on the local machine; snapshots and other observations can still reach the host Agent and model provider. A Space organizes the task but does not establish an OS sandbox or override site permissions.
The real-browser tools, by name
The real-browser side has its own concrete roster, and it sorts into four families by how the agent reaches the browser: a shared-session browser built for the job, attach routes into the Chrome you already run, vendor extensions, and no-code recorders.
ego(lite)
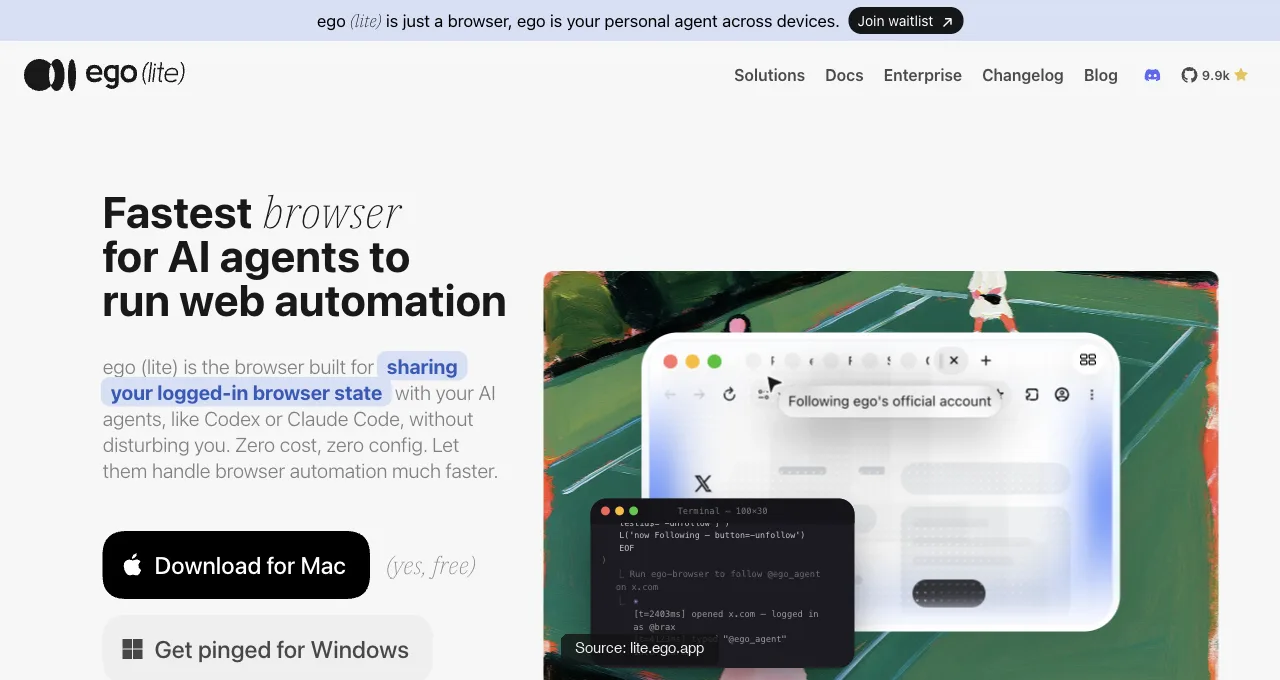
ego(lite) (free) is our own product, stated plainly: the agent runs in its own Space with its own tabs, so the window stays yours.
It's the only entry in this roster that gives the agent real sessions without giving it your window.
What that isolated Space actually returns, run today against a live page: a real ego-browser session opens a task, navigates, and comes back with only the fields asked for, no accessibility-tree dump attached.
const task = await egoBrowser.newTaskSpace('evidence-egobrowser-hn')
await task.page.goto('https://news.ycombinator.com/', { waitUntil: 'load', timeout: 20000 })
const title = await task.page.title()
const topStory = await task.page.locator('.athing .titleline > a').first().innerText()
const points = await task.page.locator('.subtext .score').first().innerText().catch(() => null)

{
  "taskSpaceId": 13
}
{
  "title": "Hacker News",
  "url": "https://news.ycombinator.com/",
  "topStory": "Qwen 3.8 27B",
  "points": "412 points"
}
Download ego(lite) for Mac, free, or see the full session model in the logged-in browser guide.
Chrome DevTools MCP auto-connect
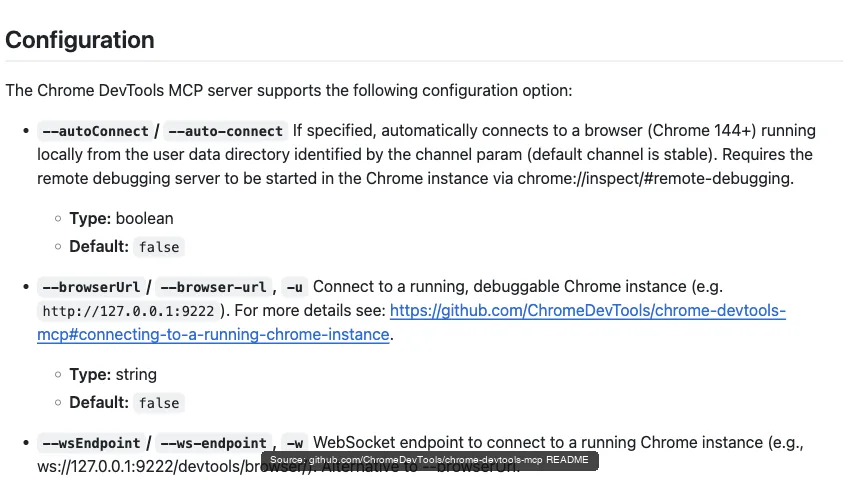
Chrome DevTools MCP auto-connect (Google, free) is the official attach route: on Chrome 144+, enable remote debugging at chrome://inspect, add the --autoConnect flag, and the agent operates inside your signed-in Chrome after a per-session permission dialog. Full sessions, real fingerprint, plus the debugging toolkit nothing else has; the cost is that it's your window being driven while it works.
Browser MCP
Browser MCP (browsermcp.io, free) is the community attach route: an extension-plus-server pair that connects Cursor, Claude, VS Code, and other MCP clients to your existing browser. Automation runs locally, uses your existing profile so your logins come along, and rides your real fingerprint; like every attach route, it drives the browser you're using, one task at a time.
Claude in Chrome and Codex for Chrome
Claude in Chrome and Codex for Chrome are the vendor-extension family: Anthropic's reads the page you're signed in to, then clicks, types, and fills forms, on all paid Claude plans; OpenAI's acts on sites where you're already signed in (its docs name LinkedIn, Salesforce, Gmail) with tasks grouped into Chrome tab groups.
Zero technical setup, mature per-site permission prompts, and two shared costs: each serves only its own vendor's agent, and each works in your window.
Axiom, Browse AI, and Simplescraper
Axiom, Browse AI, and Simplescraper are the no-code family: point-and-click recorders that capture a login-and-extract flow in a real browser session and replay it on a schedule. For a non-developer pulling one table from one portal they're the fastest first result on this page; the trade is brittleness when the site redesigns, and a hosted runner carrying your session on someone else's infrastructure.
| Tool | How the agent reaches the browser | The trade |
|---|---|---|
| ego(lite) | Separate browser inherits your sessions; agent works in its own Space via CLI | Desktop only, no headless CI; free |
| Chrome DevTools MCP | Attaches to your live Chrome via --autoConnect (Chrome 144+) | Shares your window while it works; free |
| Browser MCP | Extension + MCP server into your existing profile | Your window, one task at a time; free |
| Claude in Chrome | Vendor extension in your signed-in Chrome | Claude only, paid plans, your window |
| Codex for Chrome | Vendor extension, tasks in Chrome tab groups | OpenAI integration, configured browser connection and website permissions |
| Axiom / Browse AI / Simplescraper | Recorded point-and-click flows, replayed on schedule | Brittle on redesigns; session lives on their runner |
Read the trade column as a deployment constraint, not a universal ranking. Verify current browser support, authorized state and the task result on the route you choose.
The headless tools, by name
"Go headless" is a category, not a decision, so here's the category by name. It splits into three tiers: libraries you script against, tools built for agents specifically, and cloud fleets you rent when one machine stops being enough.
Playwright
Playwright supports Chromium, Firefox and WebKit with language bindings for Node.js, Python, Java and .NET. Locator checks and browser contexts help with timing and job state, but an auto-waited click still needs an application-level result check. Saved authentication is independent of whether a window is shown.
Headless is its native habitat in CI, and for agent use there's Playwright MCP on top of the same engine.
Puppeteer
Puppeteer provides JavaScript and TypeScript browser control. Its current documentation supports Chrome and Firefox through WebDriver BiDi, with unsupported operations listed separately; Chrome uses CDP by default and Firefox uses BiDi. It does not provide a WebKit target. Choose it for a compatible Node workflow, not because Firefox support is still beta.
Selenium
Selenium offers WebDriver tooling, multiple official language bindings and Grid infrastructure. Its BiDi APIs add bidirectional browser capabilities. Keep it when the required browser, language or existing Grid fits the task; measure the actual workload instead of inferring speed from a protocol name.
agent-browser
agent-browser (Vercel Labs, ~40K stars, Apache-2.0) is what the agent-native tier looks like: a Rust CLI with a daemon speaking raw CDP, driving a downloaded Chrome for Testing. The agent runs agent-browser snapshot to get an accessibility tree with refs like @e1, then acts on them with commands like click @e2. Sessions are deliberately isolated, output is filterable to stay token-lean, and the whole design assumes no human is watching.
Browser Use
Browser Use supplies an Agent control loop rather than a guarantee about browser identity or account access. Its execution host, profile and model determine what state and observations are available. Use a visible browser for authorized inspection or takeover when needed, and stop at access controls in either mode.
The archived demonstration below shows a perceive-decide-act loop on its recorded Browser Use and model versions. It illustrates the control flow; it is not a new November 11 run or a comparison with the other libraries.
agent = Agent(
    task="Go to https://news.ycombinator.com/ and tell me the exact title text of the #1 story on the front page, plus its points count.",
    llm=llm,
)
history = await agent.run(max_steps=8)

INFO     [Agent] Starting a browser-use agent with version 0.13.7, with provider=openai and model=gpt-4.1-mini
INFO     [Agent]   navigate: url: https://news.ycombinator.com/, new_tab: False
INFO     [tools] Navigated to https://news.ycombinator.com/
INFO     [Agent] Step 1:
INFO     [Agent]   Eval: Successfully located the #1 story title and its points count on the Hacker News front page.
INFO     [Agent]   Memory: Located the top story on Hacker News with title 'Qwen 3.8 27B' and points count '415 points'.
INFO     [Agent]   Next goal: Report the exact title text and points count of the #1 story to the user.
INFO     [Agent]   done: text: The #1 story on Hacker News front page is titled "Qwen 3.8 27B" with 415 points., success: True
Final Result:
The #1 story on Hacker News front page is titled "Qwen 3.8 27B" with 415 points.
INFO     [Agent] Task completed successfully
Browserbase and Stagehand
When the fleet outgrows your machine, the cloud tier takes over. Browserbase sells managed browser infrastructure at the scale of thousands of concurrent sessions (36.9M unique sessions in a March 2026 monthly count, 10,000+ companies), with Stagehand (23.7K stars) as its open-source SDK layering act, extract, and observe primitives over Playwright-style code.
Browserless
Browserless plays the same position with an API-first shape: REST endpoints for /screenshot, /pdf, /content, and /scrape, an /unblock endpoint for bot-detection handling, and BrowserQL for multi-step flows, callable from anything that can send an HTTP request, n8n workflows included.
The stealth layer
And one honest layer on top: the stealth ecosystem. Selenium has undetected-chromedriver and SeleniumBase; Puppeteer's puppeteer-extra-plugin-stealth is the mature classic, and playwright-extra can load its plugins; Camoufox and Patchright currently support only Playwright. Treat all of it as a moving target rather than a purchase: practitioners on r/webscraping report cases where a stealth fork got blocked while default Playwright passed.
| Tool | What it is | Where it fits headless work |
|---|---|---|
| Playwright | Cross-engine library, 4 official language families, auto-waiting | Default for CI, testing, and scripted scraping |
| Puppeteer | Chrome-first JS/TS library from the Chrome DevTools team | Lean PDF, screenshot, and crawl jobs |
| Selenium | WebDriver ecosystem, 5 documented language bindings, Grid distribution | Legacy estates and widest language/browser reach |
| agent-browser | Rust CLI + daemon, snapshot refs, isolated sessions | Agent-driven stateless automation, token-lean |
| Browser Use | Autonomous Python agent loop over direct CDP | Goal-driven scraping where steps can't be scripted |
| Browserbase | Cloud browser infrastructure; Stagehand SDK on top | Thousands of parallel sessions, managed ops |
| Browserless | Hosted browser API: REST endpoints + BrowserQL | HTTP-callable browser work from any pipeline |
These tools all require deliberate browser-state management. A fresh context, saved storage state and persistent profile each have setup and expiry costs. Inspect the actual connection before choosing a separate interactive browser route; a headless library does not forbid account continuity.
Which one has your logins?
Headless does not mean login-free. A fresh context starts empty, but Playwright can restore authentication through storageState or a persistent profile. The real difference is how much work it takes to prepare that state, reuse it, and recover after the server expires it.
On August 21, 2026, we ran each path five times against the same first-party login fixture on an M4 Mac. Playwright 1.59.1 used Chromium 147; ego(lite) was 0.4.7.1.
| State path | Reusable preparation | Median first usable | After server expiry | Security boundary |
|---|---|---|---|---|
| Fresh Playwright context | None saved; three-step login every run | 1.61s | Run login again, 0.19s | No auth file; credentials enter each run |
| Playwright storageState | Four steps, 1.81s | 1.60s | Log in and rewrite JSON, 0.26s | JSON contains session cookies and tokens |
| Playwright persistent context | Three steps, 2.39s | 1.42s | Log in inside the profile, 0.18s | Profile directory stores broader browser state |
| ego(lite) inherited session | Three steps once, 0.78s | 0.43s | Sign in once; new Spaces inherit it, 0.13s | The Space receives the account's active privileges |
All four paths completed five of five runs without a retry. With a session ready, a fresh ego(lite) Space reached the protected page in 0.43 seconds, versus 1.42 to 1.61 seconds for Playwright. Reusing any session also gives the agent that account's permissions.
Zillow stays a field observation
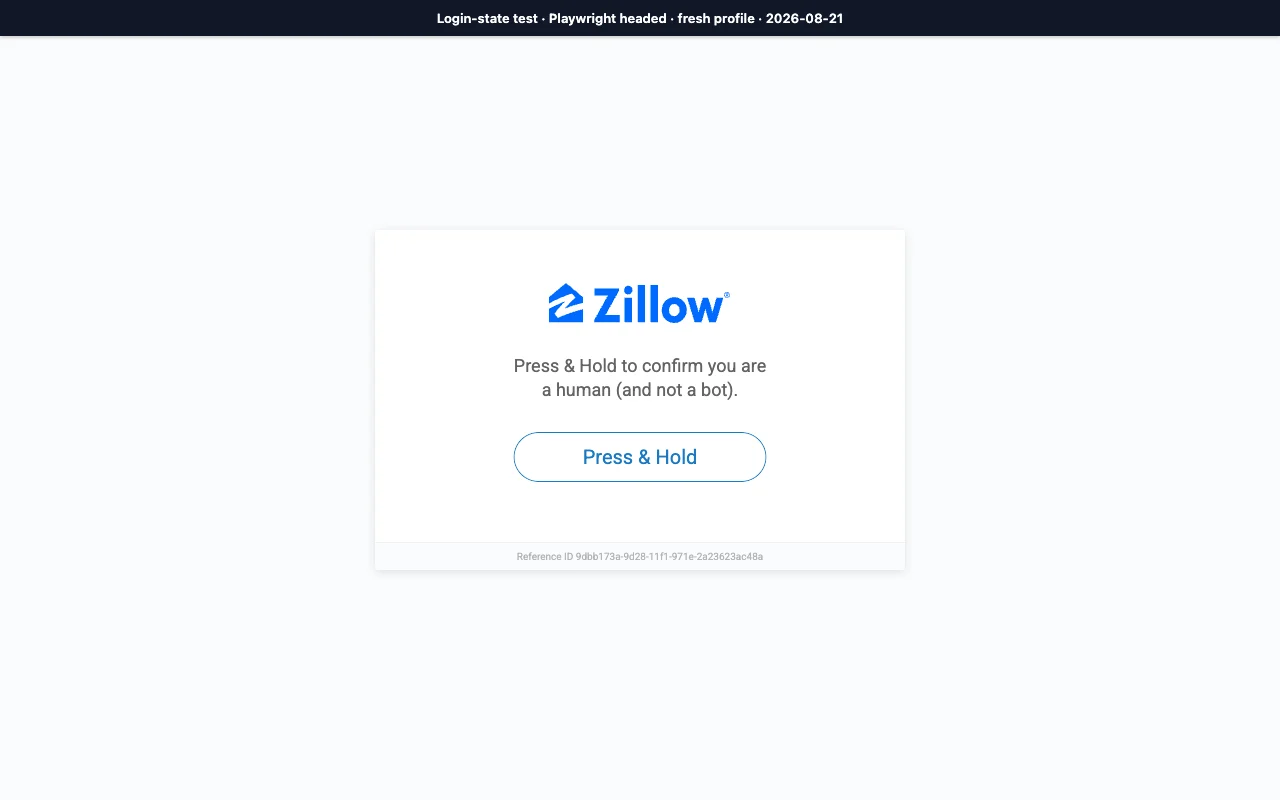
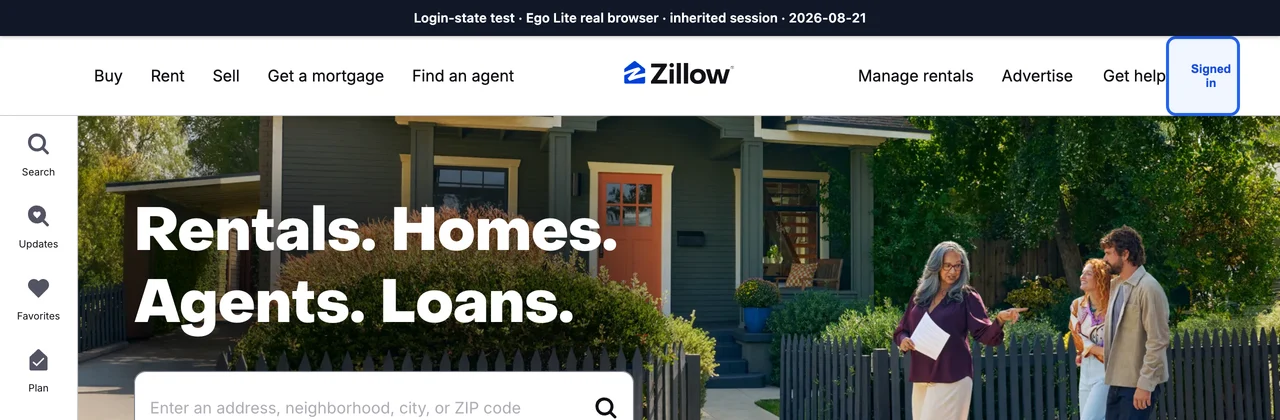
In a separate read-only run, fresh Playwright stopped at Zillow's Press & Hold screen, while ego(lite) with an inherited session reached the homepage and account menu. Read Zillow's current terms before automating. Login state, automation signals, defenses, and profile history changed together, so this remains a field observation rather than a causal benchmark.
How big is the detection gap?
Less different than it used to be, and the reason is a specific change. Chrome shipped a new headless mode (--headless=new) that runs the same browser binary as the visible one, replacing the old separate headless implementation that leaked obvious tells.
Historical headless implementations could expose different user-agent, plugin and rendering values. Current behavior depends on the selected binary, version and flags; the Chrome unification announcement does not establish that every signal now matches a desktop profile.
What still leaks is subtler and rarely lives in the user agent. Automation flags (navigator.webdriver set true unless suppressed), the absence of a real display and its device-scale quirks, timing and interaction patterns no human produces, and connection signals from datacenter IPs all remain visible to a determined defender.
Detection in 2026 is a scoring problem, not a single check: no one signal condemns you, but a stack of them does. That's why the honest framing is baseline plus behavior, not headless-bad, real-good.
Our three-mode detection test
In the archived Sannysoft case, we opened the public detector on the same Apple M4 Mac and network with Playwright 1.62.1 default headless Chromium, headed Chromium with a fresh profile, and ego(lite) with persistent state. Each configuration ran three times. Chromium versions and profile state differed, so this was not a controlled visibility-only experiment or a current access test.
| Visible signal | Playwright headless | Playwright headed, fresh | ego(lite) persistent |
|---|---|---|---|
| User agent | HeadlessChrome/151 | Chrome/151 | Chrome/150 |
| WebDriver | present (failed) | present (failed) | missing (passed) |
| Plugins | 0; PluginArray failed | 5; PluginArray passed | 5; PluginArray passed |
| Languages | en-US | en-US, en | en-US, en, zh-CN |
| WebGL renderer | SwiftShader | Apple M4 via Metal | Apple M4 via Metal |
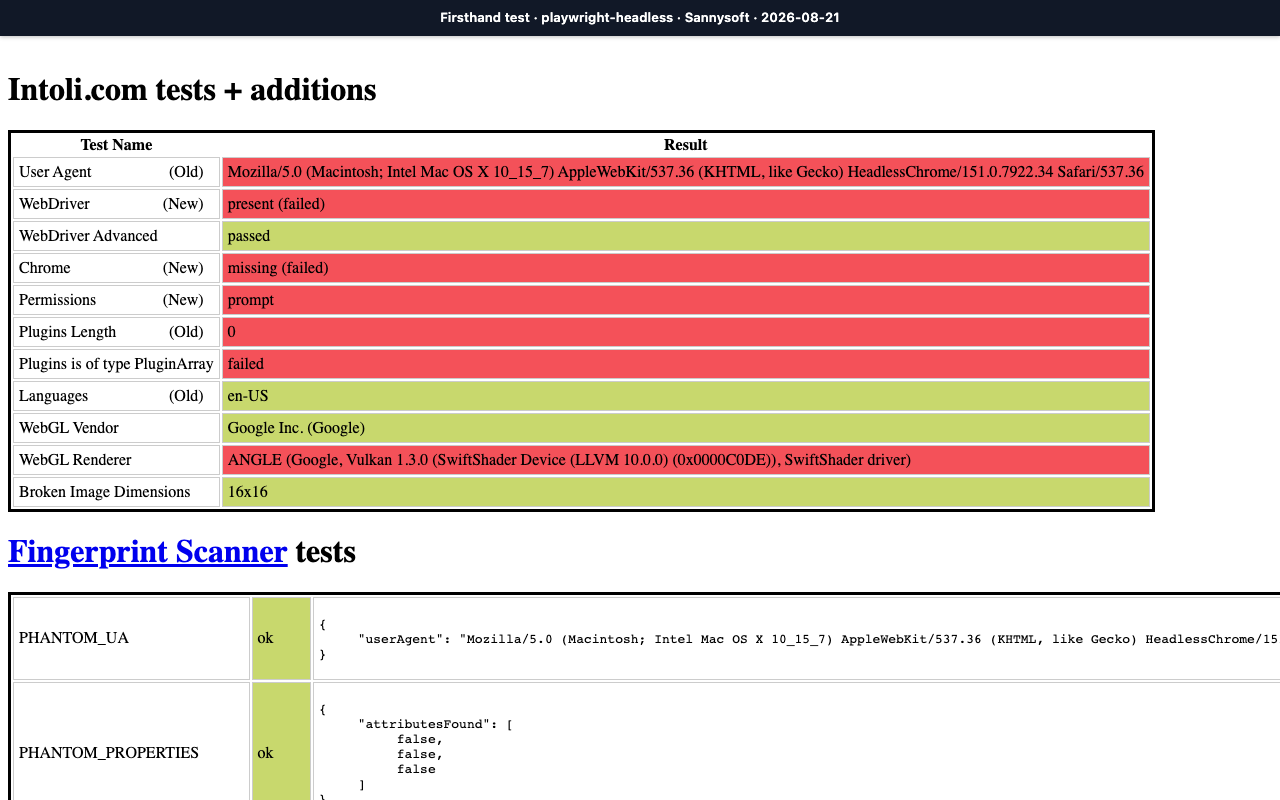
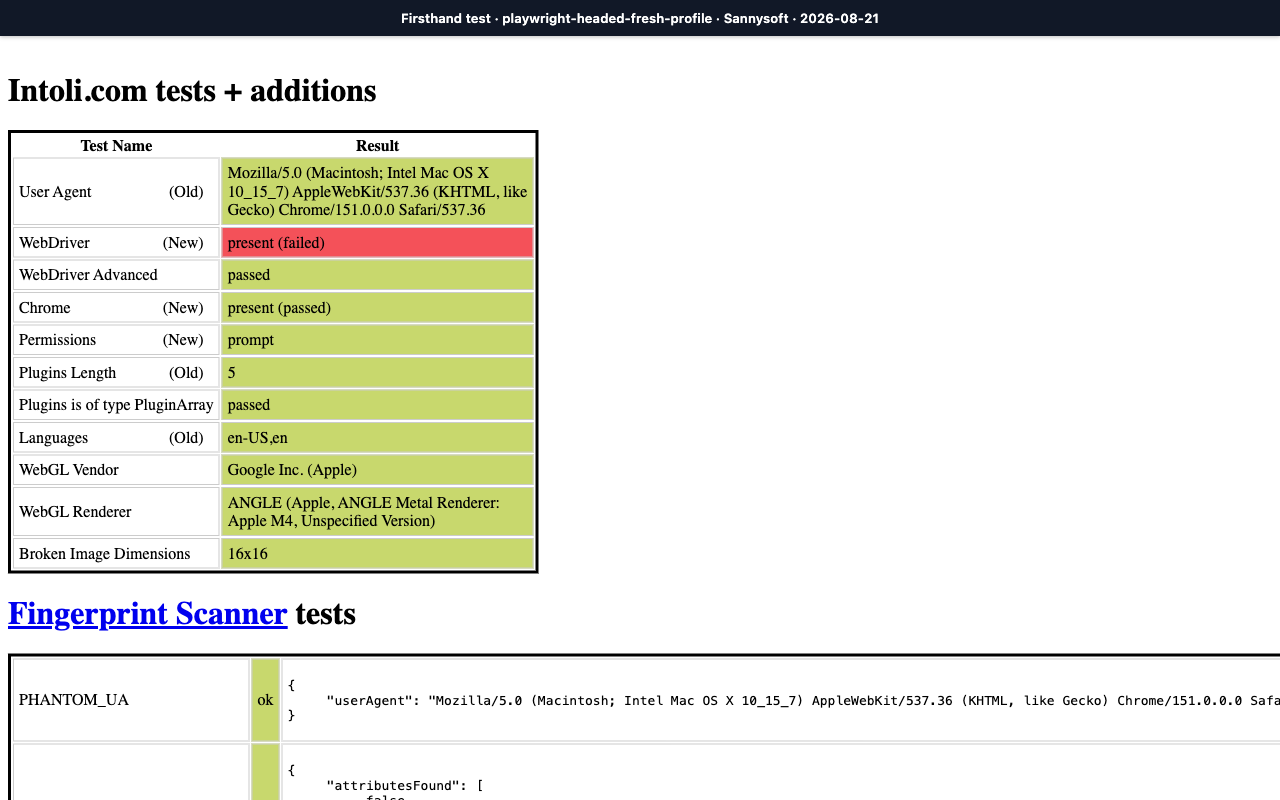
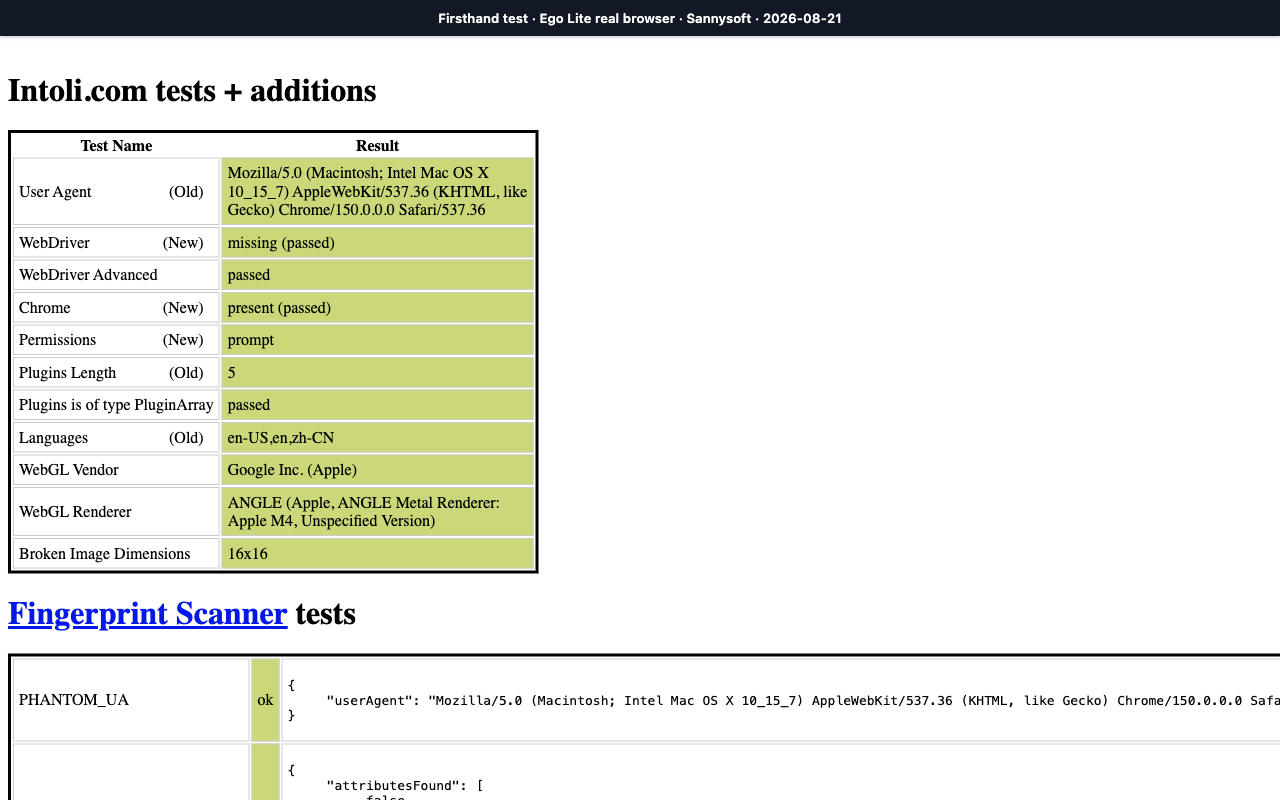
This detector case supports only the values observed on that page in those configurations. The browser builds and profile states differed, and the page did not measure account authorization, IP reputation or production task success. Do not use it to promise access to another target.
There is another important version detail: Playwright distinguishes its default Chromium headless shell from the newer headless mode available through the Chromium channel. Our default-headless result must not be generalized to every modern Chrome headless configuration. If detection matters, record the exact package, browser build, launch channel, flags, profile, network, and date.
What the tools felt like to run
Playwright was the cleaner choice for a controlled fresh-context test. The browser version and launch mode were explicit, the run could be repeated, and the screenshot was easy to capture at a fixed viewport. The friction appeared when the task crossed into account state: headed mode gave us a window, but the fresh profile was still fresh. We would need to authenticate, import state, or maintain a persistent profile before doing useful account work.
ego-browser took a different approach: it created an isolated Space and opened YC Hacker News inside ego(lite). The screenshot below shows the actual run, including the browser chrome, the agent's Browsing Hacker News cursor, and the live control panel. The agent works in its own tabs while the user can watch progress, take over, or stop the task at any time.
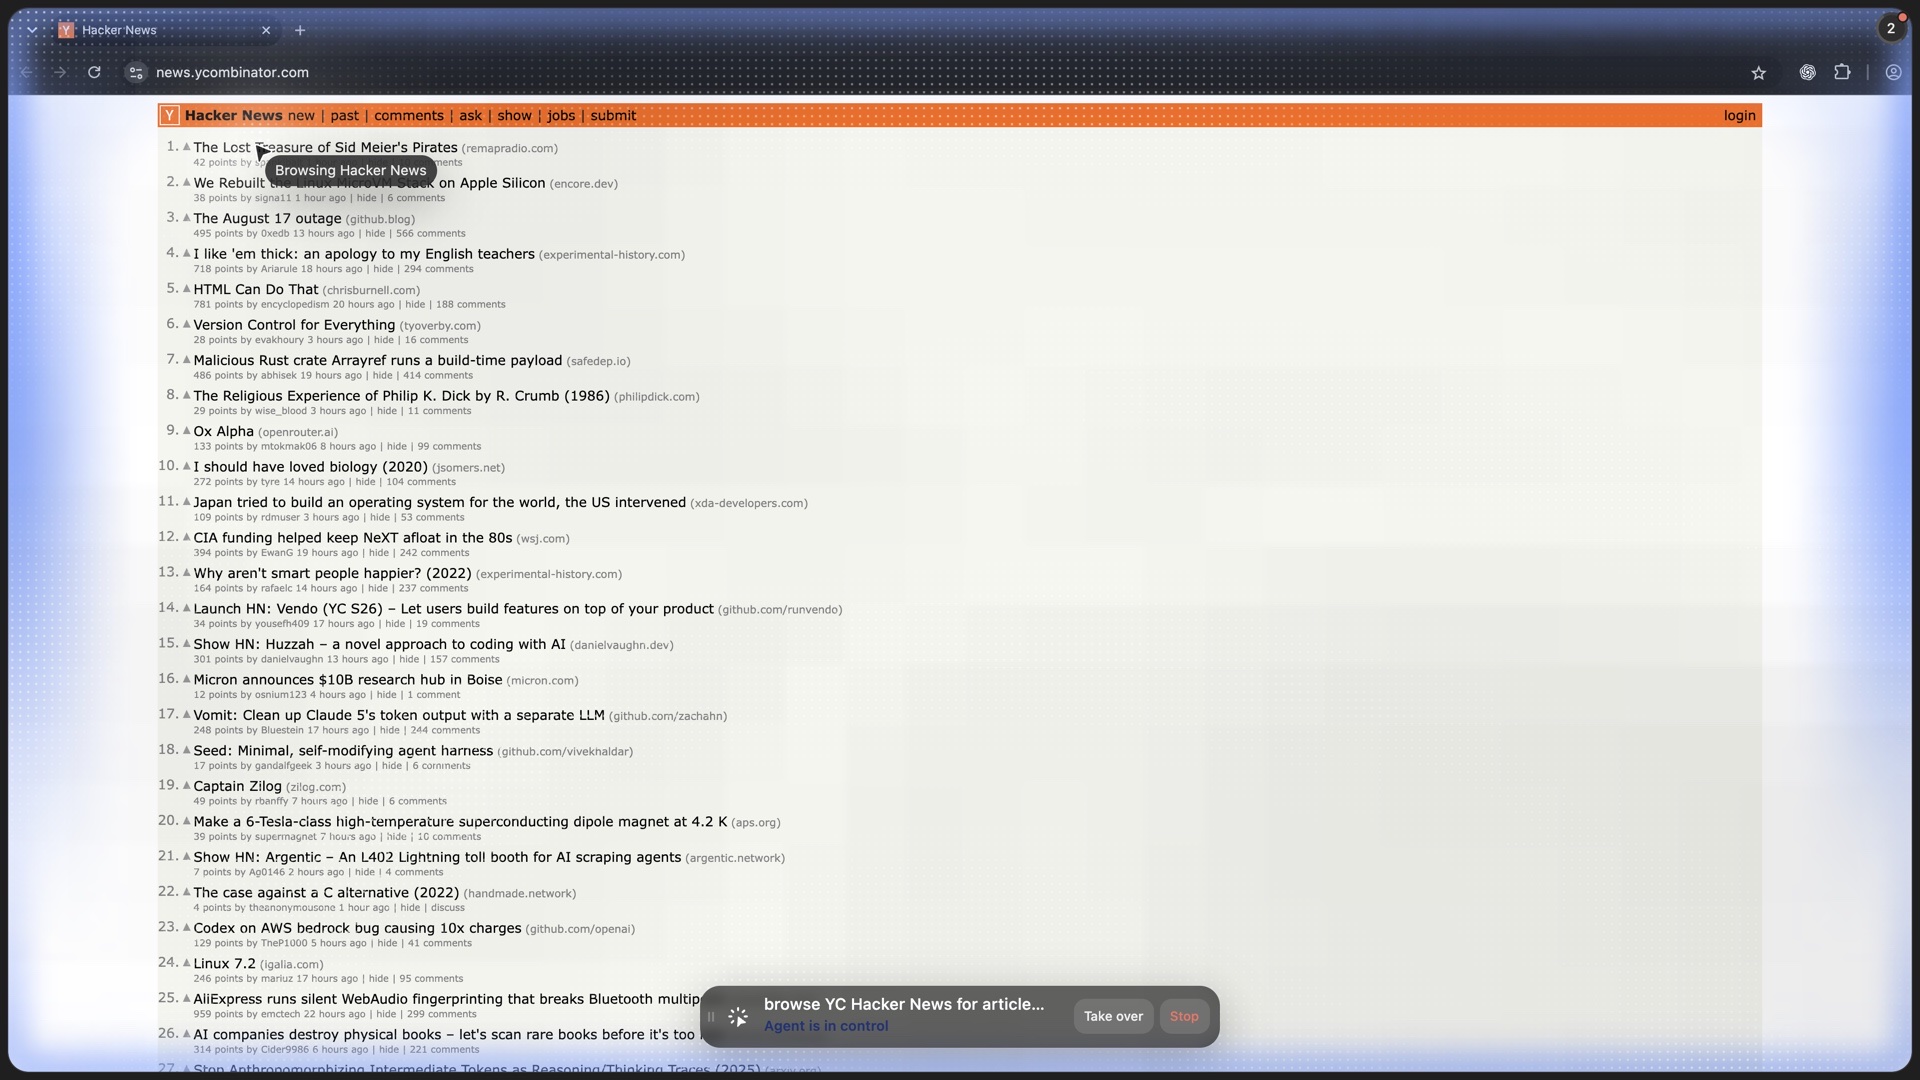
That experience also made the split between the products clearer. We would use a fresh Playwright context when a public test needs a controlled, disposable environment. When the task depends on an authorized existing session, ego(lite) skips profile recreation and lets the agent begin from the state you already prepared.
What does each cost to run?
We ran five cold starts per mode on the same M4 Mac and first-party page. Playwright 1.59.1 used Chromium 147; ego(lite) was 0.4.7.1. We recorded time, RSS, retries, and failures.
| Mode | Startup median (range) | Idle to loaded RSS | Completion median | Success |
|---|---|---|---|---|
| Default headless shell | 0.50s (0.47 to 0.73) | 238 to 263 MB | 0.64s | 5/5 |
| New headless | 0.96s (0.70 to 3.21) | 593 to 627 MB | 1.16s | 5/5 |
| Headed fresh | 1.71s (0.79 to 2.68) | 578 to 641 MB | 1.89s | 5/5 |
| ego(lite) fresh Space | 0.46s (0.43 to 0.52) | 175 to 178 MB incremental | 1.09s | 5/5 |
The default shell was the leanest full Playwright process tree at 263 MB loaded. New headless and headed reached 627 and 641 MB, only 2.2% apart. The ego(lite) Space started fastest and added 178 MB of Space processes; its row excludes the running shared app, GPU, and network processes. All 20 runs succeeded without retries.
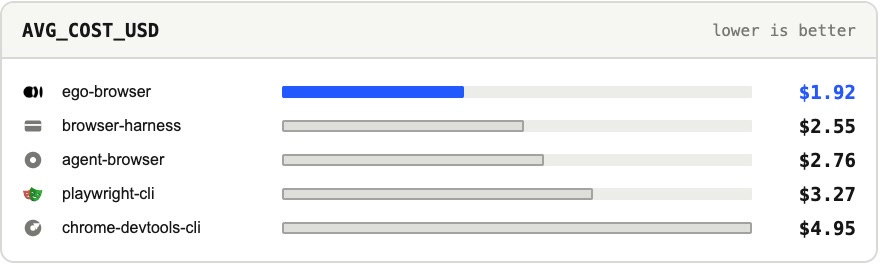
End-to-end agent cost adds another layer. In our 31-task benchmark with the same model and judge, ego-browser recorded the lowest average cost per task at $1.64. Playwright CLI recorded $3.42 and Chrome DevTools CLI recorded $4.95 under the same setup.
Which browser for which task?
The three dimensions collapse into a task lookup. Find the row that matches what you're actually doing; the pull is rarely ambiguous once the task is named honestly.
| Task | Configuration choice | Required check |
|---|---|---|
| Authorized account task | Deliberate saved state or profile connection | Verify the account and expiry in either display mode |
| Access challenge | Stop and seek a supported path | A window does not grant access |
| Interactive account work | Visible session when takeover is needed | Space organizes the task, not host isolation |
| Permitted batch collection | Headless when no visual intervention is needed | Measure actual resource and network costs |
| PDF or CI screenshot checks | Reproducible supported browser build | Assert the required output, not only process success |
Combine modes only when the task calls for it: an unattended context for repeatable jobs, deliberate authorized state for account work, and a visible session for inspection or takeover. Do not respond to a defended target by assuming that a window grants access.
Why does a scraper work locally but fail in production?
A deployment can change the browser build, network, profile, concurrency and target response. Record those inputs and compare required fields, not only HTTP 200. Start with a permitted, low-rate canary. On a challenge, 403 or 429, pause and use the supported access or retry policy; changing visibility alone is not a repair.
How should agents reuse login sessions?
Use only account-owner-authorized state. Playwright can save cookies and local storage for a new context; IndexedDB requires the indexedDB: true storageState option. Its guide warns that saved state can contain sensitive credentials. Keep it out of source control, restrict access and reauthenticate when it expires. A headed window does not create consent or prevent expiry.
What can browser fingerprints and TLS signals actually prove?
A detector reports the signals it inspects, not permission or production access. Browser build, TLS, network, account history and behavior can all differ between runs. Keep the configuration with each observation and do not turn one detector result into a site-wide pass rate. An approved API or export remains preferable to trying to defeat a target's controls.
How do you isolate profiles and cookies between agents?
Give each job deliberate account and profile ownership. A Space organizes pages and takeover; its name does not establish a separate account, OS user or host sandbox. When stronger separation is required, configure the corresponding browser, process and filesystem boundaries. Verify the active account before a write and avoid concurrent writers to one profile.
How do you detect stale pages and false success?
Bind the check to the intended record, account and time range. A fresh request can still return an old view, so use the application's version or reconciliation contract when available. A clicked button, HTTP 200 or Toast alone cannot verify a write. Preserve uncertain outcomes for a later read instead of replaying a potentially successful action.
How do you recover from headless crashes and cleanup failures?
Keep the job checkpoint separate from browser process state. On a crash, retain the last URL and trace, confirm process and profile ownership, and close only this job's resources. Before retrying a write, reconcile the record or idempotency key with the application. A browser restart does not establish that the previous submission failed.
What does an agent see, and how do extensions affect privacy?
Define which page data reaches the Agent and its model provider: snapshots, screenshots, downloads and traces may leave a local browser. Review extension permissions and data retention separately from display mode. Limit observations to authorized domains and fields; page text cannot expand the task's permissions. Local execution alone is not a privacy guarantee.
When is a real browser not the answer?
Use an authorized API or export when it provides the required structured result. Headless execution remains useful for repeatable CI, PDFs and unattended page checks. Choose a visible browser for tasks that actually need its UI or human takeover, then verify the application result. Native file dialogs have a separate control surface; see the existing native-file-dialog guide for that boundary.
How to automate native file dialogs
FAQ
What is the best headless browser for AI agents?
For most agent work it's headless Chromium driven by Playwright, because it has broad tooling, four official language families, and access to modern Chromium headless modes; Puppeteer is the leaner pick for Chrome-only jobs, and agent-browser is the CLI built for agents specifically. Firefox and WebKit headless matter when you need cross-engine coverage.
Choose the supported browser and controller for the actual task. If a target refuses access, seek an approved API, export or permission instead of choosing a mode to evade the checkpoint.
Is a browser like ego(lite) called a headed browser or a real browser?
Both descriptions are useful, but real browser is not a formal industry category. Headed only says a window is rendered, and a Playwright-launched headed Chromium can still use a fresh automation profile. In this article, real browser means the ordinary persistent browser environment a person uses: an installed profile, live sessions, and the surrounding desktop environment. ego(lite) fits that practical definition because it can inherit authorized Chrome sessions inside an isolated Space.
Can websites detect a headless browser?
Sites can observe browser, network and behavior signals in either mode. Unified Chrome headless shares its implementation with headed Chrome, but that does not promise identical signals under every build and launch setting. A detector result cannot establish permission or a production success rate.
Should Browser Use run headless or not?
Choose display mode for inspection and takeover needs; choose authorized saved state separately for account work. A headless Browser Use workflow can have saved state, and a visible one can start empty. Stop at an access challenge in either mode.
Is a real browser always safer from bans?
No browser mode guarantees freedom from restrictions. Account permissions, traffic volume, target policy and other signals still apply. Verify the supported access path and stop when the task is challenged or denied.
Does headless mean faster?
Not universally. Binary choice, workload, rendering, process sharing and network waits affect the result. The historical local resource table in this article describes its recorded configurations; it cannot establish a current speed ranking for every headless and headed deployment.
Can I share my logins with a headless browser?
Yes. Playwright can load a saved authentication state, add cookies, or launch a persistent context, but that state must be created, protected, refreshed, and debugged as it expires. If an existing authorized login is the point, a real-browser tool that inherits the user's session inside an isolated Space can remove the injection step, at the cost of being a desktop browser rather than a CI-friendly headless one.
Do AI agents need persistent computers instead of sandboxes?
They need the right combination for the job. An ephemeral sandbox is valuable for isolating untrusted, one-off code; a persistent computer is valuable when the agent must keep files, installed tools, memory, or a browser session between runs. The strongest design layers the two: isolate the workspace, persist only the state the workflow needs, and give the user a clear way to inspect, reset, revoke, or take over.
What is the difference between a headless browser and a real browser?
A headless browser runs without a visible window and is well suited to scripted, parallel work on servers. In this article, a real browser means an ordinary persistent desktop browser environment with a user-authorized profile and live sessions. The practical divide is often state management: fresh automation contexts begin empty, while an existing persistent session is already prepared.
Do stealth plugins make a headless browser undetectable?
No. Plugins like puppeteer-extra-plugin-stealth or forks like Camoufox and Patchright suppress known signals, but detection is a moving target and practitioners report cases where a stealth fork got blocked while default Playwright passed. Stealth changes a few signals; it does not buy invisibility, permission, or reliability. When a legitimate task depends on an authorized session, a real browser can reduce profile-mismatch without promising access through a control.
Choose the next step
If your choice is between a fresh Playwright workflow and an isolated session-carrying browser, read the ego(lite) vs Playwright comparison. If the task needs an existing authorized login, download ego(lite) and start in a separate Space rather than handing an agent your active browser window.